A severe cybersecurity breach involving an FBI recruitment portal has led to the unauthorized exposure of sensitive personal data and operational details belonging to thousands of current and former FBI personnel, applicants, and specialized agents.
The threat actor group known as ShinyHunters claimed responsibility for the intrusion, stating that they breached FBIJobs.gov and exfiltrated between two to three terabytes of internal data.
Extent of the Compromised Data
According to security analysts and sample datasets reviewed following the breach, the exposed records extend far beyond standard contact lists, exposing sensitive operational contexts:
- Granular Intelligence Roles: The compromised databases include internal records detailing specific job functions, field office assignments, and involvement in high-stakes counterespionage, human intelligence (HUMINT), and specialized security operations.
- Personally Identifiable Information (PII): Records contain full legal names, home addresses, phone numbers, Social Security numbers, dates of birth, and emergency contact details for agents and their immediate family members.
- Operational & Counterintelligence Risks: Cybersecurity experts and former law enforcement officials emphasize that exposing the identities, specific assignments, and family contacts of counterespionage and intelligence personnel creates severe personal security threats and provides foreign intelligence adversaries with valuable targeting data.
                         ANATOMY OF THE INCIDENT

  Exploitation of FBIJobs.gov ──► Exfiltration of 2–3 TB Data ──► Extortion Demand Issued
  (Alleged Oracle Flaw)          (PII & Intelligence Roles)      ("Retract May Advisory")
                                                                      │
                                                                      ▼
  FBI & Vendor Investigation  ◄── FBIJobs Portal Taken Offline ◄──────┘
  (Point of Breach Undetermined)
Attacker Motives and Claims
In statements released following the intrusion, ShinyHunters indicated that the attack was not driven by standard financial extortion:
- Retraction Demand: The group demanded that the FBI publicly retract a prior Public Service Announcement (PSA) that accused ShinyHunters of utilizing aggressive tactics, including harassment, swatting, and inflating their access capabilities.
- Alleged Entry Vector: The group claimed they exploited a vulnerability within Oracle’s PeopleSoft infrastructure supporting the portal to pivot into cloud environments and access stored administrative databases.
Official Response and Security Measures
The FBI confirmed that an active investigation is underway regarding unauthorized access linked to the FBIJobs.gov domain, with federal security teams working alongside third-party vendors to determine the precise vector of compromise.
As a precautionary measure, the recruitment platform was taken offline to allow forensic investigators to isolate compromised systems, remediate vulnerabilities, and assess direct security risks to affected personnel.
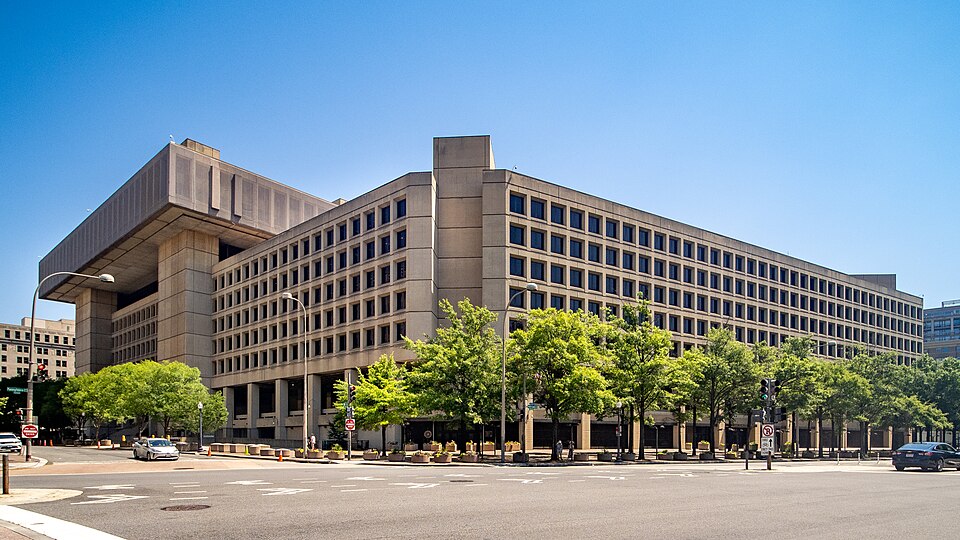
FBI Headquarters – J. Edgar Hoover Building by ajay_suresh